WEMAIDE / INSIGHTS / ENGINEERING
Human approval in AI automation: where should the system stop?
A practical architecture for placing human approval at consequential AI decisions without turning every workflow into a queue.
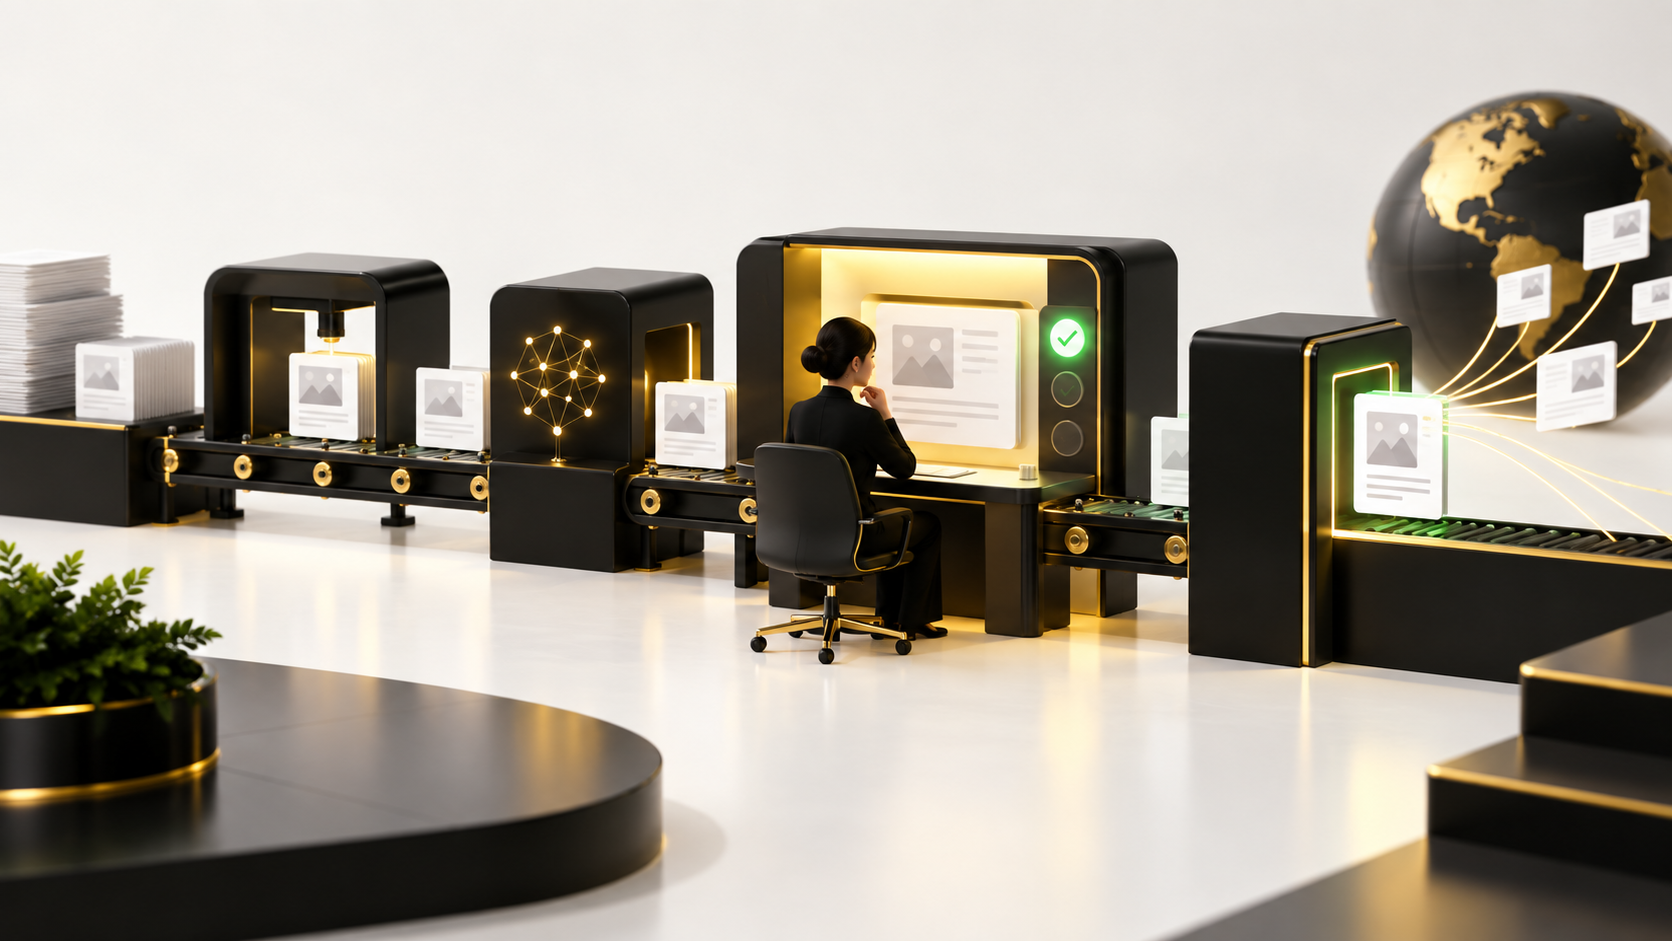
An AI system should stop for human approval before an action becomes materially consequential, difficult to reverse or difficult to explain. The approval gate belongs immediately before the external action—not at the beginning of a long run and not after the system has already sent, paid, deleted, published or changed a customer record.
Human-in-the-loop does not mean asking a person to click approve on everything. That creates review fatigue and turns automation into a slower inbox. The goal is to define which transitions the system may complete, which require a person and which must never be offered automatically.
Approval follows consequence, not novelty
A fluent AI draft may feel riskier than a fixed database update because its behavior is visibly probabilistic. But a deterministic action can have greater consequences. Moving money, revoking access or deleting records deserves protection even when ordinary code performs it. Human control should be based on impact, reversibility, permissions and evidence—not simply on whether a language model was involved.
- Externality: does the action affect a customer, public audience, partner or regulated record?
- Reversibility: can the result be undone completely and quickly?
- Magnitude: what is the maximum financial, legal, reputational or operational impact?
- Ambiguity: is the system interpreting intent or choosing among legitimate alternatives?
- Evidence: can the reviewer see the exact inputs, proposed action and reason for stopping?
Place the gate at the last responsible moment
Let the system collect context, run safe analysis and prepare an artifact before it interrupts someone. The reviewer should receive a complete proposal at the point where permission changes. Approving research is not the same as approving the email generated from it. Approving a content topic is not the same as approving the final platform-specific post.
collect → analyse → draft → validate → [human approval] → external action → record outcomeSeparate proposal generation from the decision to act. In a workflow requiring strict approval, permission should apply to the exact content, media and destination that were reviewed. Material changes should require another review. Those are recommended controls; a Ready status alone does not enforce them.
Approval is not a mood attached to a task. It is permission for one defined action using one inspectable artifact.
A concrete example: reviewing content in Content Operator
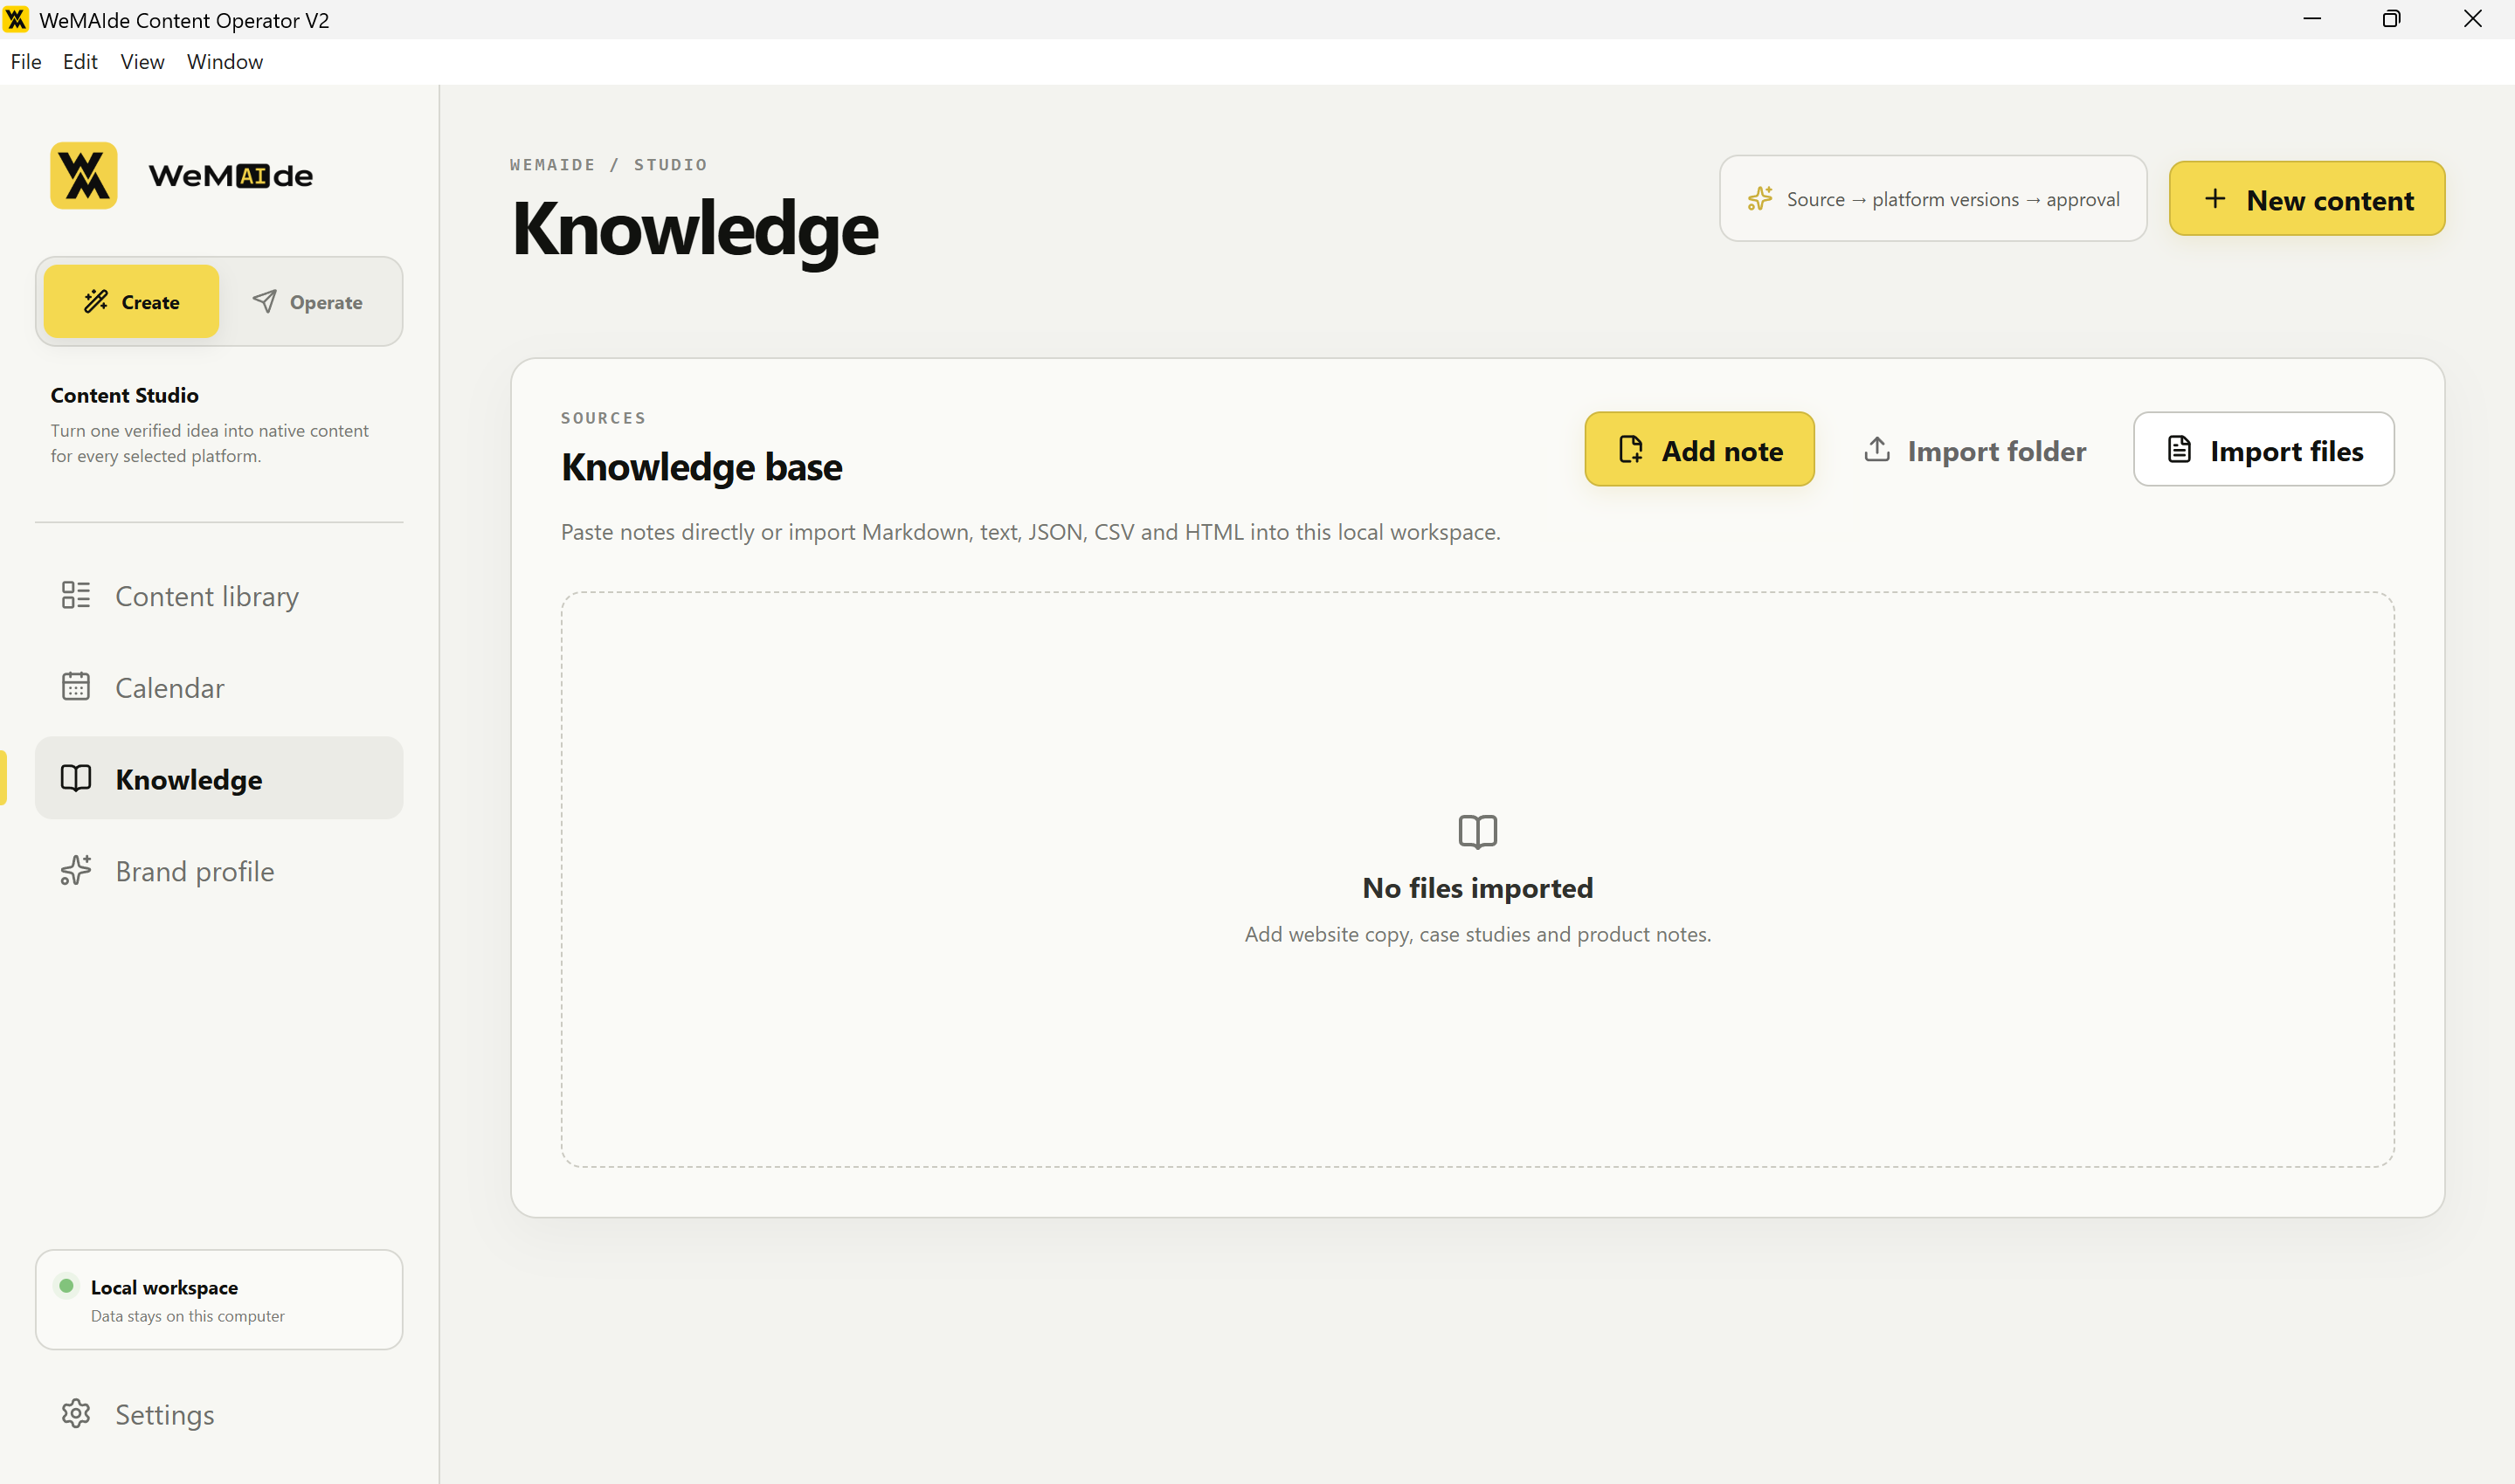
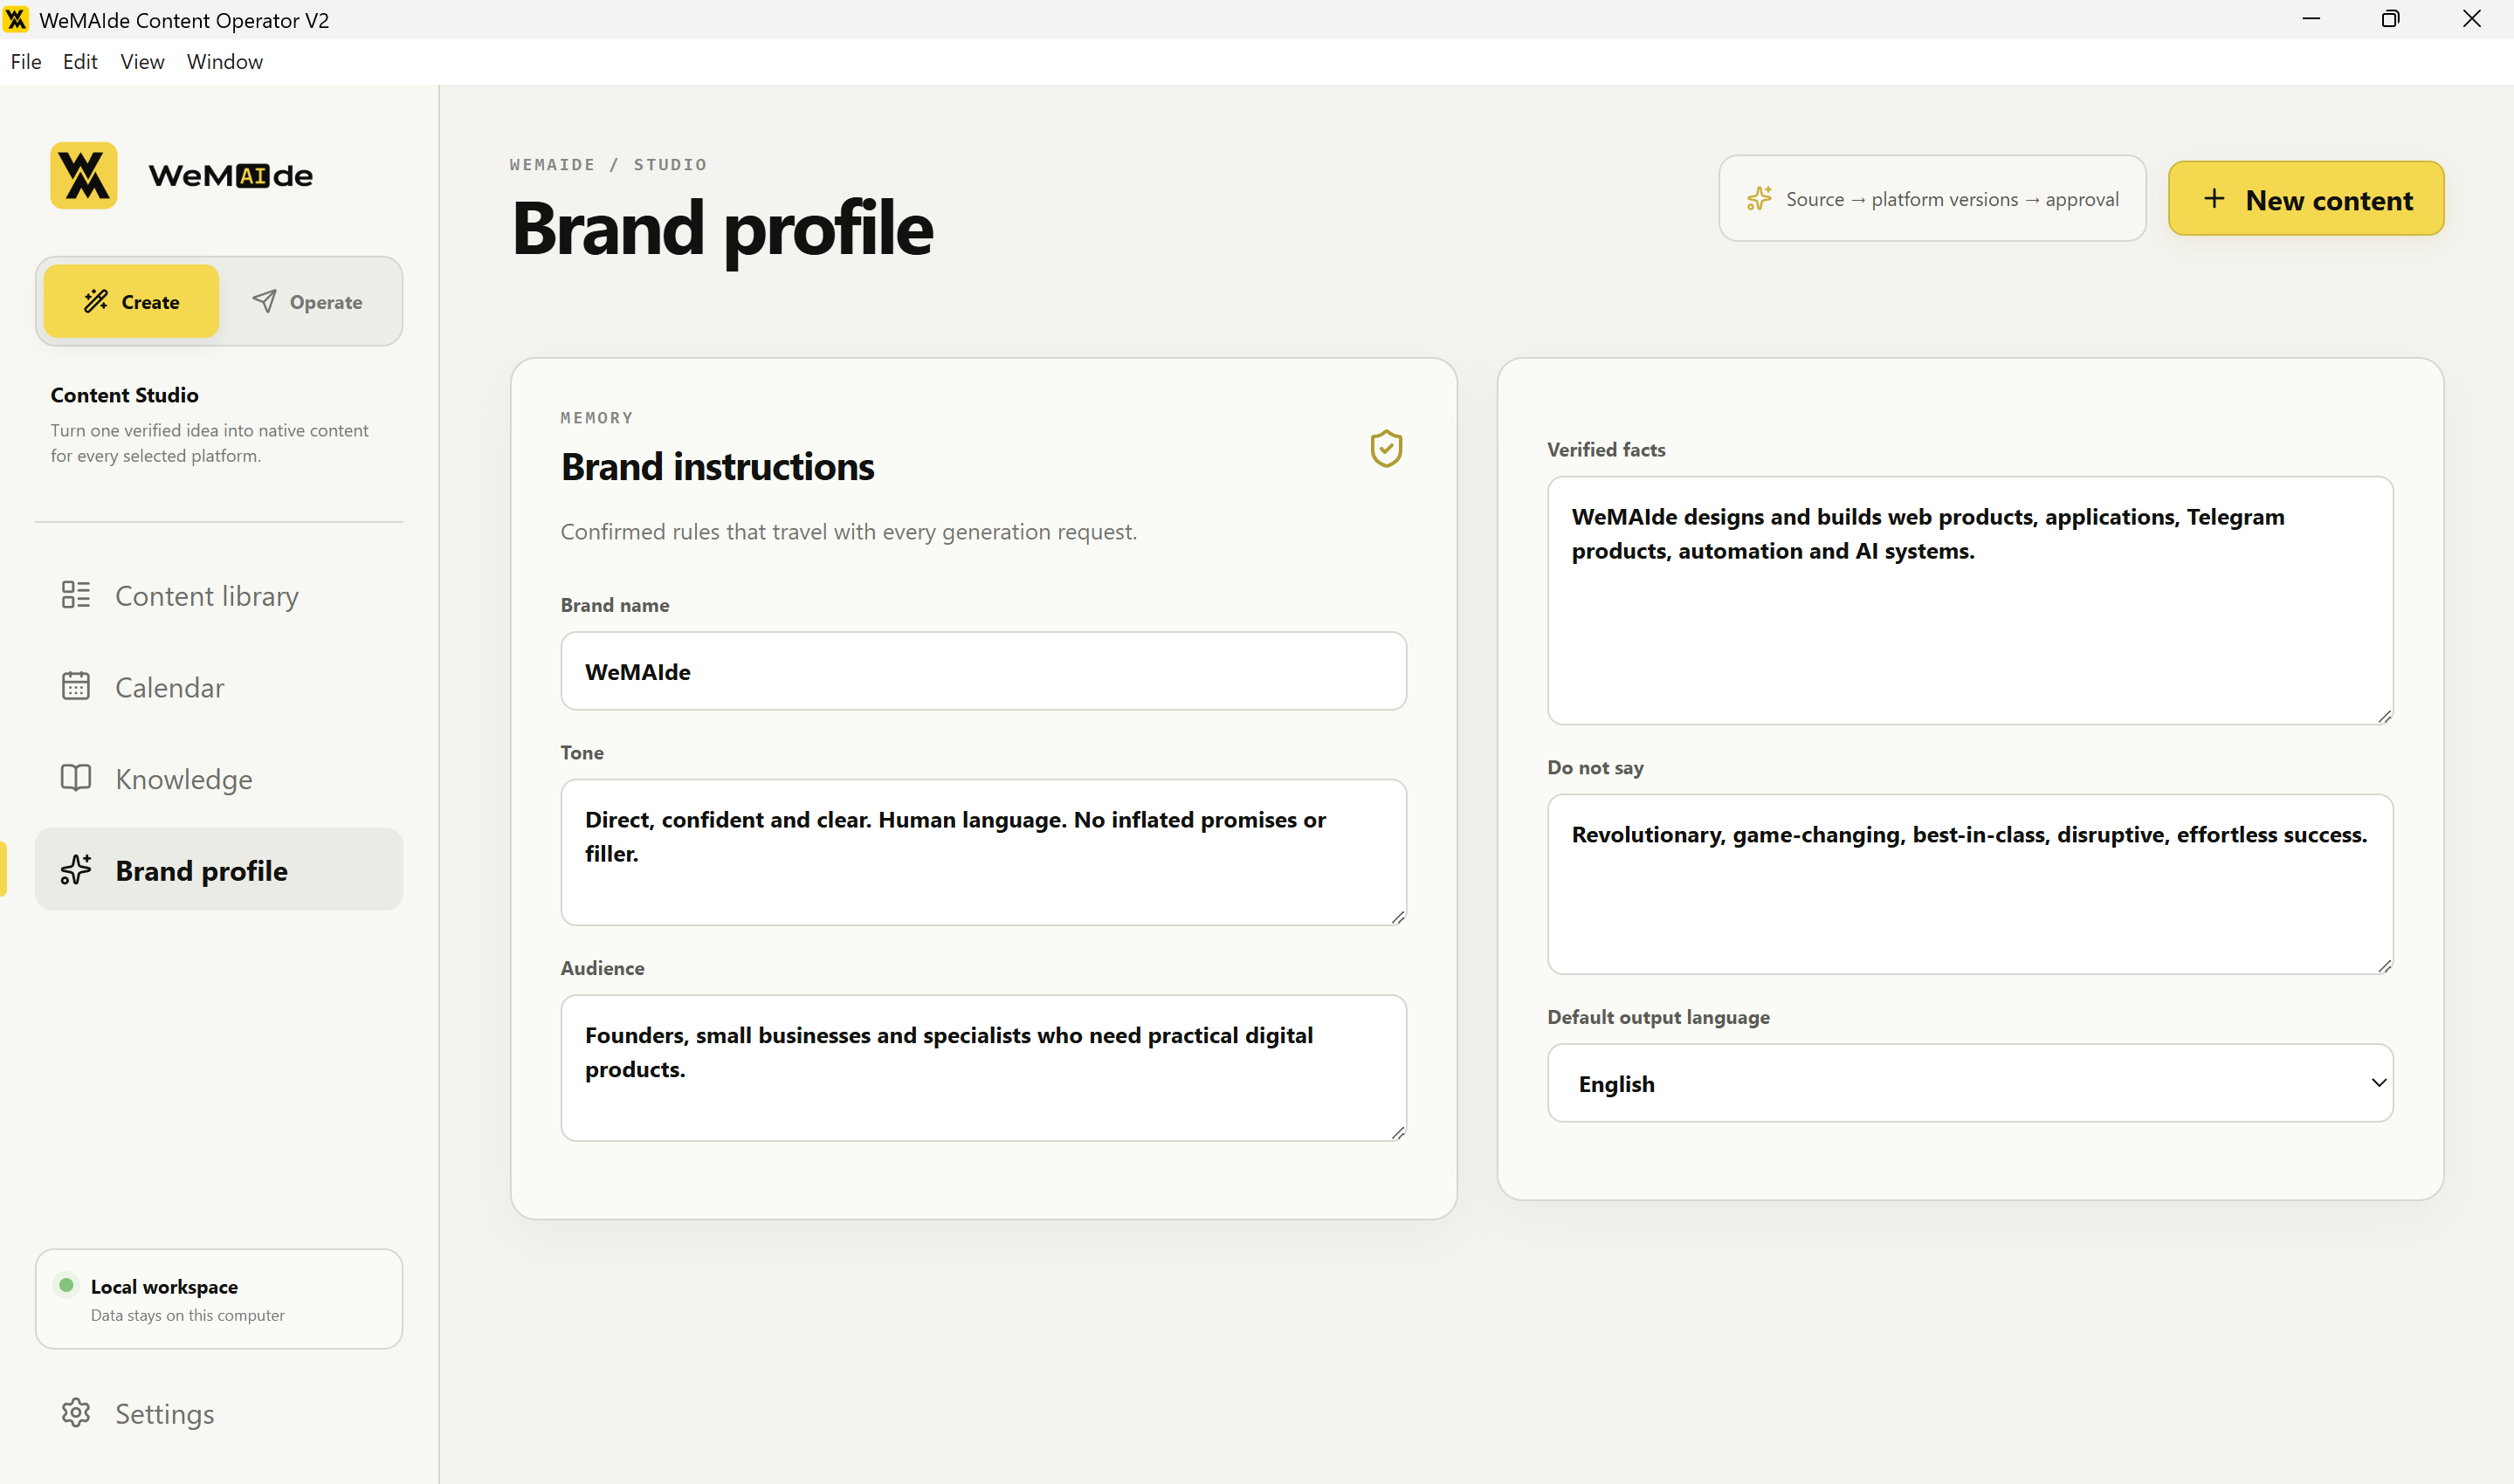
Content Operator is WeMAIde’s Windows content workspace, available in beta. An operator supplies an idea and selected brand knowledge, then generates separate drafts for the selected platforms. Each generated version starts as a draft. The operator can inspect the text, edit it and mark it Ready; publishing is a separate, explicit action through a supported connection.
Editing the text or requesting an AI rewrite returns that item to draft and removes its scheduled date. The calendar supports editorial planning; automatic background publishing is not enabled. The beta does not provide a complete approval receipt bound to a content digest, destination identity, reviewer and expiry. That stronger design is a recommendation, not a feature claim.
Current beta: idea + selected knowledge → platform draft → text review → Ready → explicit Publish now
Recommended stronger control: reviewed proposal → scoped approval receipt → execution check → outcome record| Field | Example to inspect |
|---|---|
| Proposed action | Publish one reviewed product announcement |
| Destination and revision | Example company LinkedIn page; draft revision 3 and its attached image |
| Verified source | Approved release note: CSV export is available in the desktop beta |
| Claim to remove | Saves every team 10 hours each week — no evidence supplied |
| Decision | Approve this proposal, request changes or reject |
| Re-review triggers | The text, media, destination or material source facts change |
| Execution receipt | Confirmed result and platform identifier or URL when returned; unresolved results stay uncertain |
Test the control by changing the draft after approval, replacing the destination and calling the execution boundary without a valid decision. A protected workflow should stop each unauthorised variation. Also simulate an accepted external action whose response is lost: reconcile the uncertain outcome before repeating it. These are acceptance checks for the stronger architecture, not test results claimed for the beta.
What the reviewer needs to see
- The exact action: send, publish, update, pay, delete, grant or schedule.
- The destination, account, audience and timing.
- The proposed payload or a readable before-and-after diff.
- The evidence and source data that informed the proposal.
- Policy warnings, confidence limits and unresolved ambiguity.
- Expected cost and whether the action is reversible.
- A clear approve, reject or edit path—plus an expiry time for stale approvals.
A reviewer should not need to reconstruct the run from logs in another system. If the approval screen hides the actual recipient, changed fields or source evidence, the human is present but cannot meaningfully supervise the action.
Use risk tiers instead of one global mode
A practical system can route actions through several levels. Low-impact, reversible steps can run automatically. Medium-impact actions can run within explicit limits and be reviewed through sampling. High-impact or ambiguous actions stop before execution. Prohibited actions are unavailable regardless of model confidence.
- Automatic: read-only retrieval, formatting, tagging or reversible internal updates inside clear limits.
- Bounded automatic: actions within amount, audience, data and frequency thresholds, with logs and alerts.
- Approval required: public publishing, customer communication, financial commitments, permission changes and destructive operations.
- Always manual: actions the organisation has not made safely reviewable or does not authorize the system to propose.
Design escalation before autonomy
An agent must know how to stop well. Escalation triggers should include repeated tool failures, missing required evidence, conflicting policies, exceeded budgets, uncertain identity and any request outside the approved scope. The handoff should preserve the attempted steps and gathered context so a person continues the work instead of starting again.
OpenAI’s agent guidance recommends human intervention when failure thresholds are exceeded and for high-risk, sensitive or irreversible actions. NIST’s AI Risk Management Framework similarly calls for human oversight processes, roles and responsibilities to be defined, assessed and documented according to organisational policy. Both point to the same engineering conclusion: oversight has to be part of the workflow design, not a disclaimer added after deployment.
Approval is only one control
Do not make the reviewer the only safety mechanism. Before an item reaches approval, the system should validate schemas, permissions, budgets, destinations and policy constraints. After execution, it should store the approved artifact, actor, timestamp, external response and final state. Idempotency protects against a double send; retries should resume the approved action rather than regenerate a different one.
- Guardrails reduce predictable invalid proposals before review.
- Permission scopes limit what tools can do even after a model asks.
- Versioned approvals prevent silent edits after a person has checked the result.
- Idempotency and state machines prevent duplicate or impossible transitions.
- Logs and outcome monitoring reveal patterns that individual approvals cannot.
When can approval be reduced?
Remove a gate only after the team has evidence that a bounded class of actions performs reliably, exceptions are detected and recovery works. Narrow automation by destination, amount, content type or user group before removing review globally. Continue sampling outcomes and make it possible to return the class to approval-required mode when conditions change.
The mature goal is not maximum autonomy. It is the highest useful level of automation at which responsibility remains clear. A well-designed stop is not a failure of the agent. It is one of the system’s most important successful outcomes.
Sources and related material